Forensic, not antivirus
It does not alter or quarantine files, and every result is reportable, so it fits evidence handling.
Malware discovery for forensic investigators
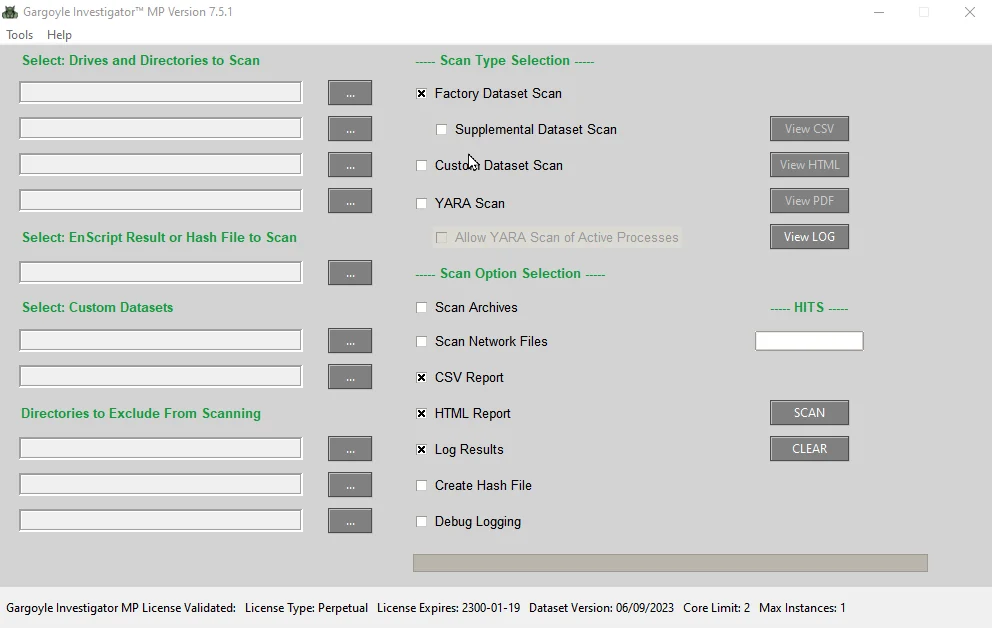
Gargoyle Investigator MP runs a rapid search for malicious programs on evidence media and gives clues to the activities, motives and intent of a suspect. It is built for forensic laboratories, law enforcement, field investigators, private investigators and enterprise security teams.
01 Questions to ask
02 Why Gargoyle Investigator MP
Gargoyle Investigator MP keeps everything users know from Gargoyle Investigator and improves it: a new, modern codebase, faster scans and better archive and file-format processing. It simplifies breach and malware triage and lets you search quickly for known contraband, hostile programs and lost or leaked corporate assets.
It does not alter or quarantine files, and every result is reportable, so it fits evidence handling.
Many law enforcement and government agencies scan their forensic workstations with Gargoyle to counter claims that the workstation introduced malware.
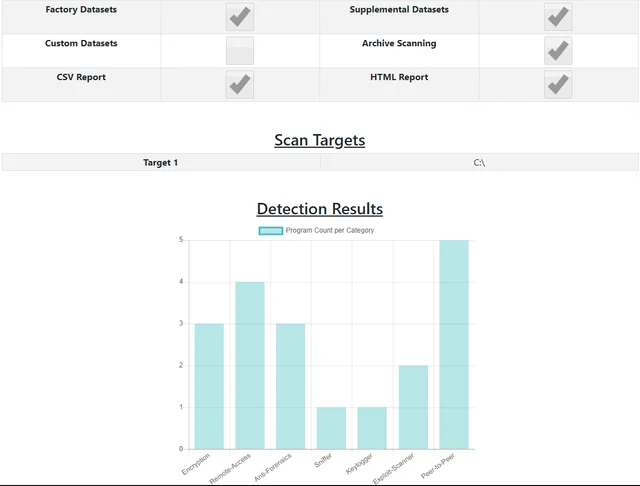
Finding encryption, anti-forensics, password crackers or remote-access tools on evidence media tells you what a suspect could do.
Add YARA rules and custom hash datasets for newly disclosed malware or other files of interest; whitelist what is not relevant.
03 Reports
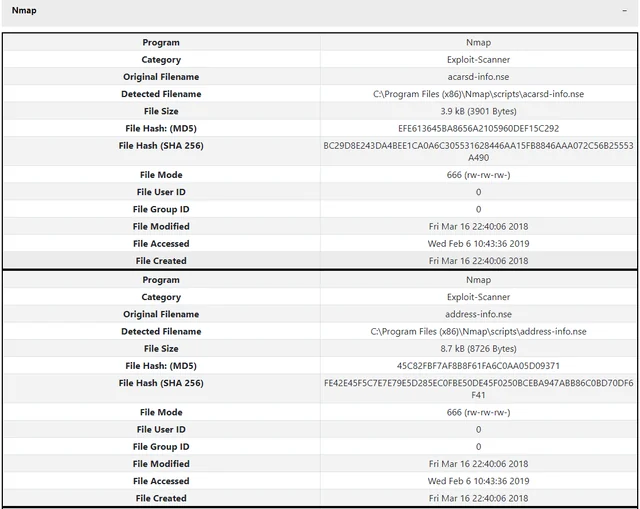
Comprehensive reporting in CSV, HTML and log formats.
04 What it detects
WetStone searches for and maintains a malware repository for each of these categories, with monthly dataset updates.
05 Integrations
Gargoyle scans comma-separated files of MD5 hashes, so it can check hash results for malicious code or cyber weapons from almost any forensic collection platform.
An EnScript ships with Gargoyle Investigator MP. It exports a hash file from EnCase in the format Gargoyle scans.
Pick a Forensic Explorer export in the hash file section and Gargoyle formats it before it scans.
06 Editions
A scanner licensed for one dedicated workstation, made for digital forensic lab investigations. Cost-effective and easy to use.
Licensed on a USB 3.0 flash drive for field investigations and incident response. It can be shared securely across a DFIR team.
07 Specifications
| Windows desktop |
|
|---|---|
| Windows Server |
|
| You receive |
|
| License: ESD | Electronic software download for one system. Subscription license, not transferable. Basic license is 2 cores; more cores available. |
| License: FLASH | 16 GB USB 3.0 device for field investigations and use on more than one system. Limited to 2 cores. |
Gargoyle has proven to be an important contribution to the suite of digital forensics software.
Library
Articles from WetStone’s library, written by our CTO.
Request a demo
Demos are arranged by a person, not a bot. Tell us what you need to find and a WetStone representative will set up a walkthrough.