Find the threatshidden in your files
Malware, steganography and DICOM threat
detection software, built since 1998.
01 Who it’s for
Built for the people who have to find it
For more than two decades WetStone has protected enterprises and helped law enforcement. Three kinds of teams rely on it.
Hospitals, imaging centers and PACS teams
PACS and the DICOM standard store and move every image your radiology team reads.
- SecureDICOM
Law enforcement and forensic labs
Your findings have to stand up in court.
- Gargoyle Investigator MP
- StegoHunt MP
- US-LATT
Enterprise SOC, DFIR and insider threat teams
Insiders already have access, and the tools they use, from encryption programs to steganography and peer-to-peer sharing, often look legitimate.
- Gargoyle Enterprise Manager
- StegoEnterprise
- TDIR Bundle
- US-LATT
02 Products
Detect. Acquire. Investigate.
Each tool does one job well: find malware and dual-use programs, expose hidden data, collect live evidence, or keep medical images clean.
SecureDICOM
Imaging securityFinds malware and hidden data inside DICOM medical images, checks each file against the DICOM standard and quarantines bad files.
02Gargoyle Enterprise Manager
Insider threat detectionGargoyle at enterprise scale: scans endpoints and servers for malware and the potentially unwanted programs insiders use, on demand or on a schedule.
03Gargoyle Investigator MP
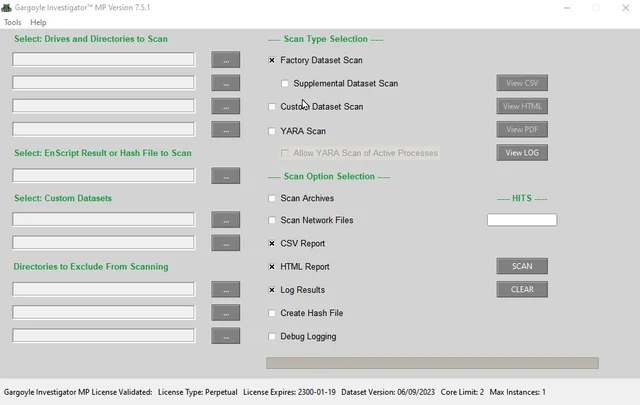
Malware discoveryForensic malware scanner for labs, law enforcement and incident responders. Finds hacker tools, PUPs and malware and explains what a suspect could do.
04StegoEnterprise
Steganography detectionScans millions of images and other carrier files across your infrastructure and flags files that may hide information or malware.
05StegoHunt MP
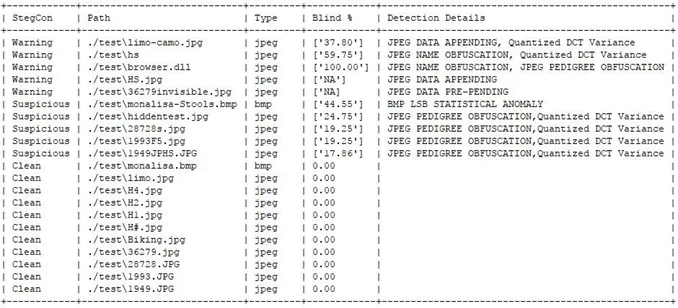
Steganography detectionDetects steganography programs, data hiding tools and the carrier files that hold hidden payloads. Includes StegoAnalyst and StegoBreak.
06US-LATT
Live acquisition and triageUSB Live Acquisition and Triage Tool: collects volatile evidence from a live Windows system at the scene, before it is lost.
07TDIR Bundle
BundleGargoyle Enterprise Manager, US-LATT, Gargoyle Investigator MP and StegoHunt MP in one detect, acquire and investigate workflow.
03 Threat defense and incident response
One workflow, from first alert to findings
The TDIR Bundle puts the tools in order, so your DFIR team starts with evidence instead of guesses.
Acquire
US-LATT
Rapid collection and first analysis on live Windows systems during or right after an incident: physical memory, screenshots, running processes and disk images, before volatile data is lost.
US-LATTInvestigate
Gargoyle Investigator MP
Assess the intent, motives, sophistication and capabilities of the insider or attacker.
Gargoyle Investigator MPUncover
StegoHunt MP + StegoAnalyst
If GEM found data hiding programs, or you suspect steganography anyway, StegoHunt MP triages the evidence US-LATT collected and StegoAnalyst confirms the hiding method.
StegoHunt MP04 Track record
Trusted in labs, agencies and enterprises
Gargoyle has proven to be an important contribution to the suite of digital forensics software.
Program Director, Computer & Digital Forensics, Champlain College
- 2021Gargoyle Investigator LE achieved VICS-certified status from Project VIC International, a high standard for detecting and classifying child exploitation material.
- 2019NOAA awarded WetStone a multi-year contract to provide steganalysis products and services for its Operational Secure Ingest Service (OSIS) project.
- SCGargoyle Investigator was named one of the Top 20 cyber security products of the past 20 years by SC Magazine.
- 2018Recognized on the Cybersecurity 500 list by Cybersecurity Ventures at the Cyber Investing Summit.
- HotSelected as a "Hot Cybersecurity Company to Watch" by Cybersecurity Ventures in multiple years.
Some of our clients
- NOAA
- Honeywell Aerospace
- Iron Mountain
- Iowa State University
- Abu Dhabi Police
- Dubai Police
05 Library
From our library
Research and how-to articles on DICOM security, steganography and forensic practice.
Using WetStone’s Gargoyle Investigator™ MP to Validate Forensic Workstations and Counter Contamination Claims
Diagnostic Imaging Files as a Cyber Threat Vector: Extending the Case for Specialized Protection
Stegomalware’s Growing Role in Modern Cyberthreats: Trends, Techniques, and the Need for Advanced Detection
06 Request a demo
See WetStone on your own data
Demos are arranged by a person, not a bot. Tell us what you need to find and a WetStone representative will set up a walkthrough.
- Toll free1-844-493-8786 (1-844-4-WETSTN)
- Phone571-340-3469
- Salessales@wetstonelabs.com
- Supportsupport@wetstonelabs.com
- Office2983 John F. Kennedy Blvd, Suite #200, Jersey City, NJ 07306