Dual-use tools
Keyloggers, encryption and data exfiltration utilities help a malicious insider stay hidden.
Solutions / Enterprise SOC & DFIR
Insiders already have access, and the tools they use, from encryption programs to steganography and peer-to-peer sharing, often look legitimate. WetStone helps your SOC and DFIR teams find them across endpoints, screen the data you take in, and respond with the evidence intact.
01 Who this is for
02 The risk
Keyloggers, encryption and data exfiltration utilities help a malicious insider stay hidden.
Third-party feeds and files can hide malicious content with steganography.
Shutting down a machine destroys volatile data such as memory and network sessions.
03 The tools
Gargoyle at enterprise scale: scans endpoints and servers for malware and the potentially unwanted programs insiders use, on demand or on a schedule.
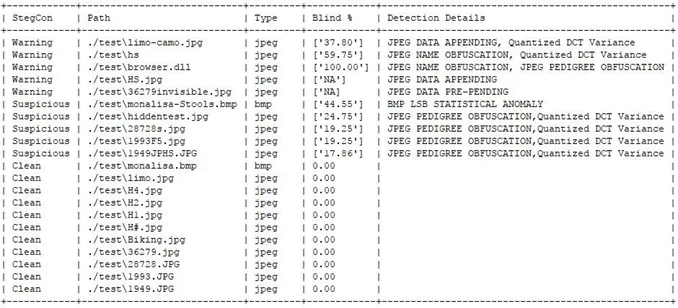
02Scans millions of images and other carrier files across your infrastructure and flags files that may hide information or malware.
03Gargoyle Enterprise Manager, US-LATT, Gargoyle Investigator MP and StegoHunt MP in one detect, acquire and investigate workflow.
04USB Live Acquisition and Triage Tool: collects volatile evidence from a live Windows system at the scene, before it is lost.
Request WetStone’s paper by email.
04 Library
Articles from WetStone’s library, written by our CTO.
Request a demo
Demos are arranged by a person, not a bot. Tell us what you need to find and a WetStone representative will set up a walkthrough.